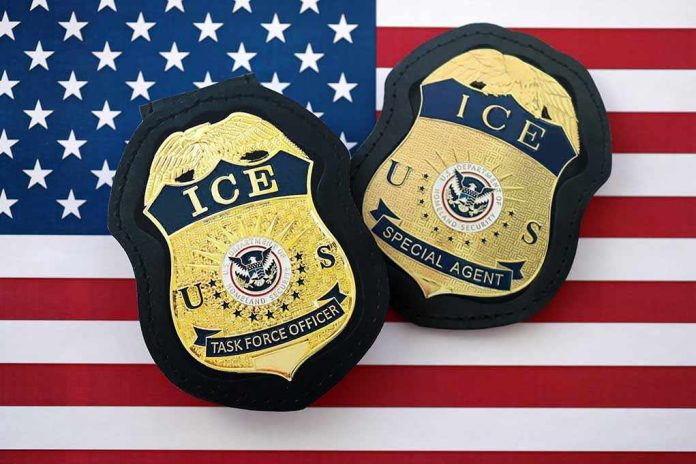
Public-sector cybersecurity fails most consequentially not when secrets leak, but when identity and organizational data about people in sensitive jobs becomes searchable at scale; that is exactly what happened when a cache describing more than 41,000 Department of Homeland Security personnel surfaced online, a personnel exposure rather than a classic state-secrets breach.
The Short Version
- A searchable database describing tens of thousands of DHS staff and contractors was published online, confirming a large personnel-data exposure across ICE, CBP, USCIS, and DHS headquarters.
- DHS acknowledged a potential breach and moved to protect affected employees while investigating scope and method, rather than disputing that an incident occurred.
- An activist group said the data was obtained through DHS’s Okta single-sign-on; attribution remains asserted by the group, not confirmed by DHS.
- The exposed fields skew toward professional identity and access details; claims about deeper operational compromise exceed what the public record proves.
What the exposure was — and was not
The public record supports a clear baseline: a large, searchable database appeared describing more than 41,000 DHS personnel, spanning multiple components and roles. Journalism that reviewed the materials found names, job titles, offices, work email addresses and phone numbers, and assignments; the corpus included ICE, CBP, USCIS, HSI, the Federal Protective Service, CISA, and headquarters staff. Distributed Denial of Secrets hosted the files, while a separate actor created a user-friendly front end to query them — the distinction matters because publication and interface were not controlled by the same entity. DHS did not deny the incident; it said it was aware of a potential breach and was working swiftly to address it and protect personnel, a posture consistent with an active response rather than a refutation.
Equally important is what remains uncertain. The aggregate “41,000” figure reflects records, not a deduplicated census of unique current employees; the hosting outlet described the set as non-comprehensive and subject to inaccuracies carried forward from source systems. The fields appear largely professional rather than private — workplace identities and access attributes rather than home addresses or classified files — though any appearance of undercover or investigative roles elevates risk even when only work identifiers are exposed.
How it likely happened: identity, not perimeter
The group styling itself the “Department of Peace” claimed it obtained access through DHS’s Okta single-sign-on (SSO) service, a plausible — if unconfirmed — path given how identity providers concentrate trust and session tokens across many systems. In recent breach telemetry, compromised credentials are the leading initial-access vector; Verizon’s 2025 Data Breach Investigations Report attributed 22% of confirmed breaches to credential abuse, with third-party involvement, including external identity services, doubling year over year to 30%. An SSO foothold does not necessarily imply compromise of the identity provider itself; it could be as simple as valid-but-stolen credentials, weak second factors, session hijacking, or abuse of delegated admin apps. Once authenticated, directory exports, group memberships, and application entitlements can be enumerated quickly — exactly the ingredients visible in this exposure set.
That mechanism matters for prevention. If the attacker’s advantage came from identity, compensating controls must live there too: phishing-resistant multifactor (for example, FIDO2 keys or platform-bound passkeys), conditional access enforcing device health, just-in-time elevation, and tight audit on SCIM provisioning and service-account scopes. The pattern is ordinary in modern breaches; the scale of consequence here comes from which organization’s identities were enumerated, not the novelty of the technique.
Why the stakes are high even when data is “work only”
Some observers minimize risk because home addresses or Social Security numbers were not publicly documented in the set. That is shortsighted. For law enforcement, immigration, and intelligence-adjacent personnel, the binding of a real person to a role, unit, office location, and access group can jeopardize operations and personal safety. DHS’s concern centered on undercover investigators and field officers; the White House’s border policy lead emphasized that agents have families — a rhetorical shorthand for threat modeling in the physical world. Even if only workplace identifiers leak, adversaries can correlate them with social media, court filings, vendor databases, and public records to build targeting dossiers. Risk is a mosaic; one tile can be enough to finish the picture.
There is also institutional risk. Exposed group memberships and application entitlements can provide an attacker’s shopping list for subsequent intrusions; knowledge of who can reach which systems, or which liaisons sit between components and external partners, reduces reconnaissance cost and increases the likelihood of convincing social-engineering pretexts. Reason’s coverage highlighted ICE liaisons to military commands — exactly the kind of connective tissue that, if verified, aids both adversaries and watchdogs in mapping interagency flows.
Attribution and authenticity: what the record actually supports
Two lines often get conflated in public debate: whether the dataset is real enough to matter, and who, precisely, obtained it. On authenticity, mainstream outlets reviewed the database, contacted individuals listed, and described consistent, work-relevant fields — strong circumstantial validation short of a DHS forensic report. On attribution, the “Department of Peace” took public credit and described an Okta-based path; reporters echoed that claim, sometimes too uncritically. But attribution to the group is not independently proven in the public record; there is no DHS technical report or DOJ filing tying intrusion artifacts to the entity that issued the statement. The right reading is straightforward: treat the exposure as real and operationally serious, while treating the perpetrator’s identity as an open question pending official forensics.
Precision also tempers expansive claims about scope. Some accounts allude to covert programs or surveillance tech; what is publicly documented with confidence are professional identities, contact details, assignments, and access-group information. Assertions of broader operational compromise remain uncorroborated by the available evidence and should be hedged accordingly.
Alleged data breach involving the US Department of Homeland Security.
A threat actor leaked records on more than 41,000 DHS employees and contractors.
Data reportedly includes names, work contact details, office locations and system access records, allegedly from an Okta SSO…
— BreachNews (@BreachNewsHQ) October 29, 2026
What effective remediation looks like
Responding well requires two timelines: rapid containment and structural reform. On day zero, rotate credentials, invalidate sessions, re-enroll phishing-resistant MFA, and audit identity-provider logs for anomalous consent grants, token minting, and directory export events. Notify affected personnel, especially those in undercover or high-threat roles, and coordinate with protective services on immediate risk mitigation. DHS publicly said it was taking protective measures while investigating, which aligns with this playbook.
On the structural side, agencies should move beyond username-password-MFA patterns that crumble under credential theft. Mandate hardware-bound authenticators for all privileged and field roles; segment directory exports; enforce least-privilege on app scopes; and require device posture checks before granting access to administrative portals. Expand red-team exercises to include identity-provider attack paths and consent phishing. Finally, treat personnel-directory data as sensitive operational information: instrument rate limits, watermark exports, and monitor for mass enumeration — because even when data is “just work,” its aggregation is an operational asset to adversaries.
How to read incidents like this going forward
Three questions define the public understanding of breaches and are too often blurred. First, was there an exposure with real-world consequences? Here, yes: a large, queryable set of DHS personnel identity and role data was published, and DHS acted as if the risk were genuine. Second, who did it and how? A credible, technically ordinary identity-based path was asserted by self-identified perpetrators, but official attribution remains open. Third, what was the substantive harm? For high-risk government roles, the aggregation itself is harm — it simplifies targeting, complicates undercover work, and can chill operations. The right posture for readers — and for policymakers — is to demand narrow precision on the unknowns while refusing to downplay the knowns simply because the leaked fields look mundane. In the modern threat landscape, identity is the perimeter; when identity maps leak, the perimeter moves with them.
Sources:
facebook.com, washingtonpost.com, thedailybeast.com, wtsp.com, reason.com, endtimeheadlines.org, verizon.com